Uncover Vulnerability.
Build Resilience.
Drive Strategy.
At VRS Tangent, we operate at the critical intersection of technology risk and enterprise growth. We know that for modern security leaders, robust governance and verifiable data provenance are never operational bottlenecks—they are the foundational architecture for secure digital transformation.
We empower your enterprise to uncover hidden vulnerabilities across your attack surface, engineer resilient systems against evolving threat vectors, and execute security-by-design strategies that fuel sustainable growth.
We coordinate defenses where classical security systems intersect with emerging AI architectures.
IS Audit (Information Systems Audit)
Conducting systematic evaluation of IT infrastructure, access controls, data provenance lifecycles, and operational systems to uncover vulnerabilities and optimize your control environment.
Read moreCompliance
Aligning internal policies, identity management, and data handling practices with strict corporate governance requirements, zero-trust principles, and international security benchmarks.
Read moreRegulatory Audit
Delivering independent, evidence-based assessments that verify strict adherence to sector-specific legal standards, statutory regulations, and industry mandates without sacrificing operational agility.
Read moreTraining
Providing structured workforce enablement, comprehensive security awareness programs, and specialized workshops designed to fortify your internal risk culture at every layer.
Read moreResilience & Strategy
Developing proactive business continuity and disaster recovery (BCDR) strategies, incident response playbooks, and strategic risk frameworks that enable your organization to withstand and rapidly recover from disruptions.
Read more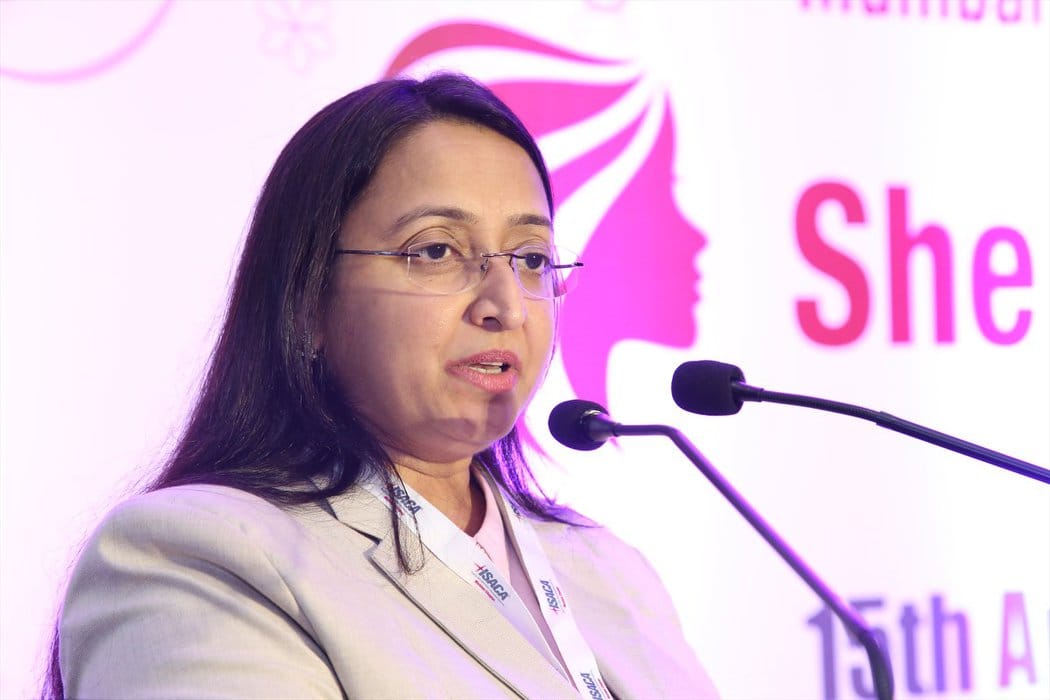
Dr. Farhat Jummani, Ph.D.
Dr. Farhat Jummani brings a distinguished combination of academic rigor and hands-on governance expertise to VRS Tangent. Holding a Doctorate in Computer Science with a specialized focus on Cybersecurity and Information Security, Dr. Jummani serves as a trusted advisor to enterprise leadership navigating the complex frontier of digital risk and data privacy.
- Areas of Specialization: AI Governance (ISO 42001) & Information Security Lead Implementation | Auditing (ISO 27001)
- Credentials: CISA, CDPSE, ISO 27001:2022 LA & LI, ISO 42001:2023 LI,
CSX-F, CIAI, CIAS, CIAD
Upcoming Courses
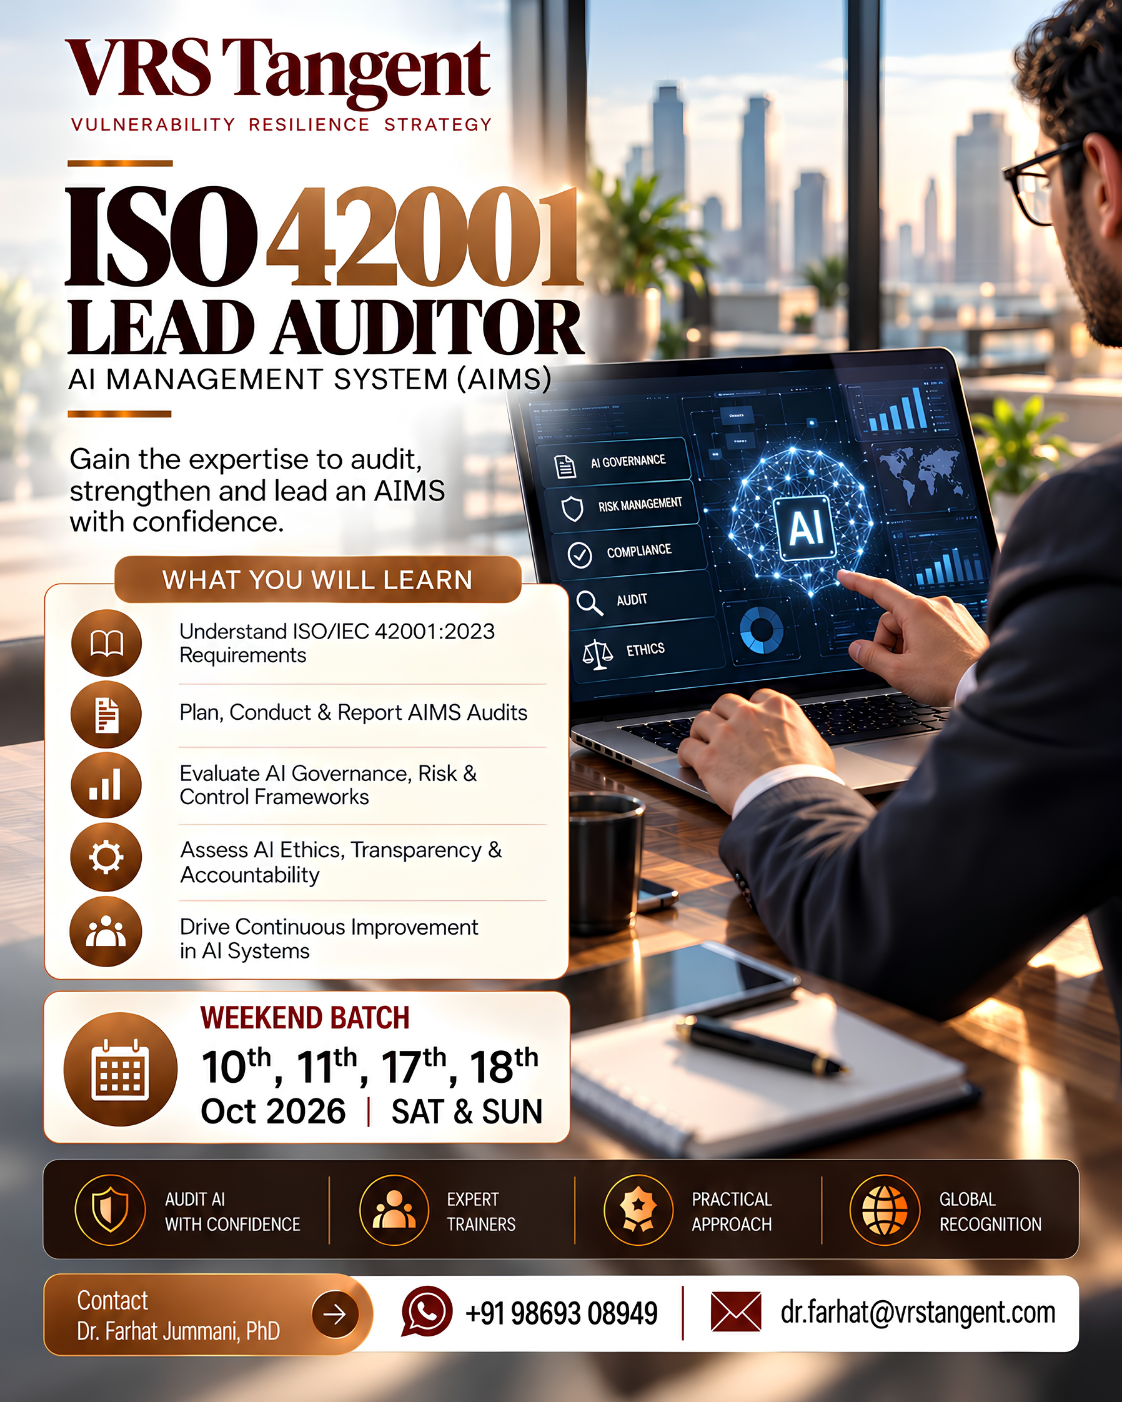
ISO 42001:2023 Lead Auditor
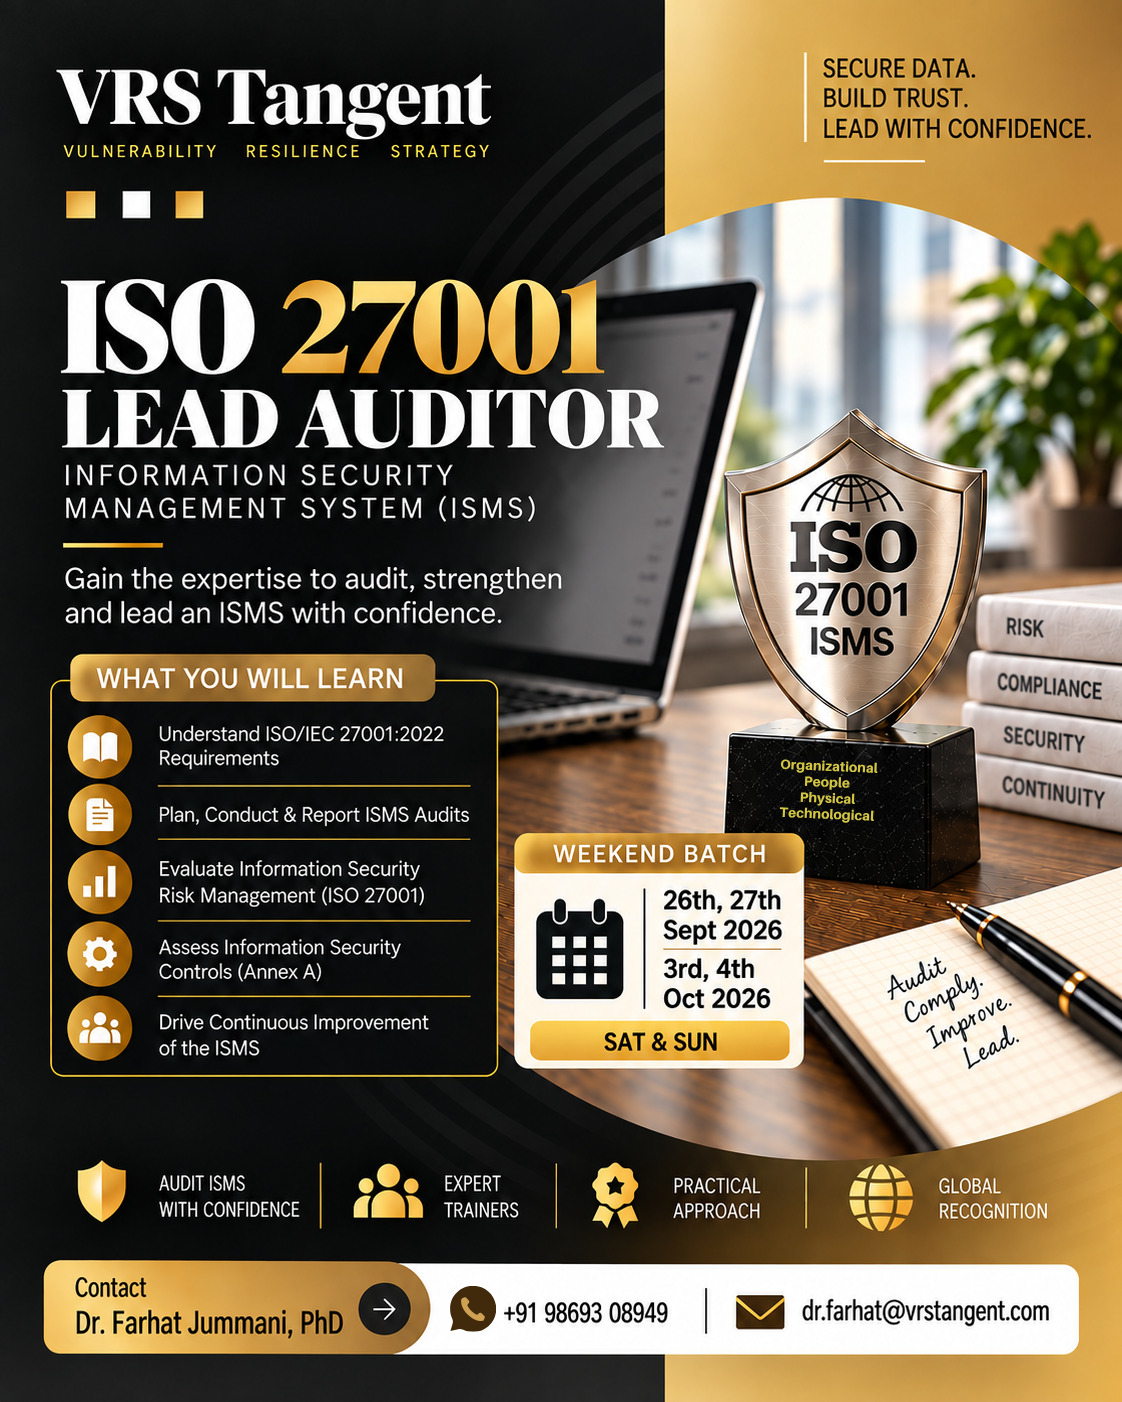
ISO 27001:2022 Lead Auditor
Frequently Asked Questions
Explore answers to common questions regarding our cybersecurity advisory, ISO compliance frameworks, and executive training.
VRS Tangent provides executive cybersecurity advisory, ISO 27001 (Information Security Management System) Implementation, Auditing, ISO 42001 (Artificial Intelligence Management System) implementation, compliance, and enterprise threat modeling. We also deliver certified executive masterclasses and master sessions for technology leaders.
We conduct end-to-end gap analyses, design tailored risk classification systems, structure documentation and controls, and run mock readiness audits. Our approach ensures sustainable compliance that withstands rigorous third-party audits rather than superficial checklist compliance.
ISO/IEC 42001 is the world's first certifiable standard for Artificial Intelligence Management Systems (AIMS). It provides governance frameworks for organizations developing, deploying, or utilizing AI systems—addressing ethical considerations, algorithmic bias, data lineage, and AI security risks.
Our masterclasses and training sessions are curated for CISOs, CIOs, Chief Risk Officers, Internal Auditors, Compliance Directors, and senior technology professionals who need pragmatic insight into emerging cyber architectures, regulatory mandates, and AI governance.
You can initiate an inquiry via our Contact page. Our leadership team will arrange an initial discovery discussion to evaluate your organization's risk profile, governance goals, and engagement scope.